imbajin opened a new pull request, #3307:
URL: https://github.com/apache/hugegraph/pull/3307
## Purpose A custom truststore previously allowed a trusted certificate with the wrong server identity. HTTPS requests now retain OkHttp's default hostname verification: trust alone is insufficient, and a matching DNS or IP Subject Alternative Name is required. The public `HostNameVerifier(String)` constructor remains available. 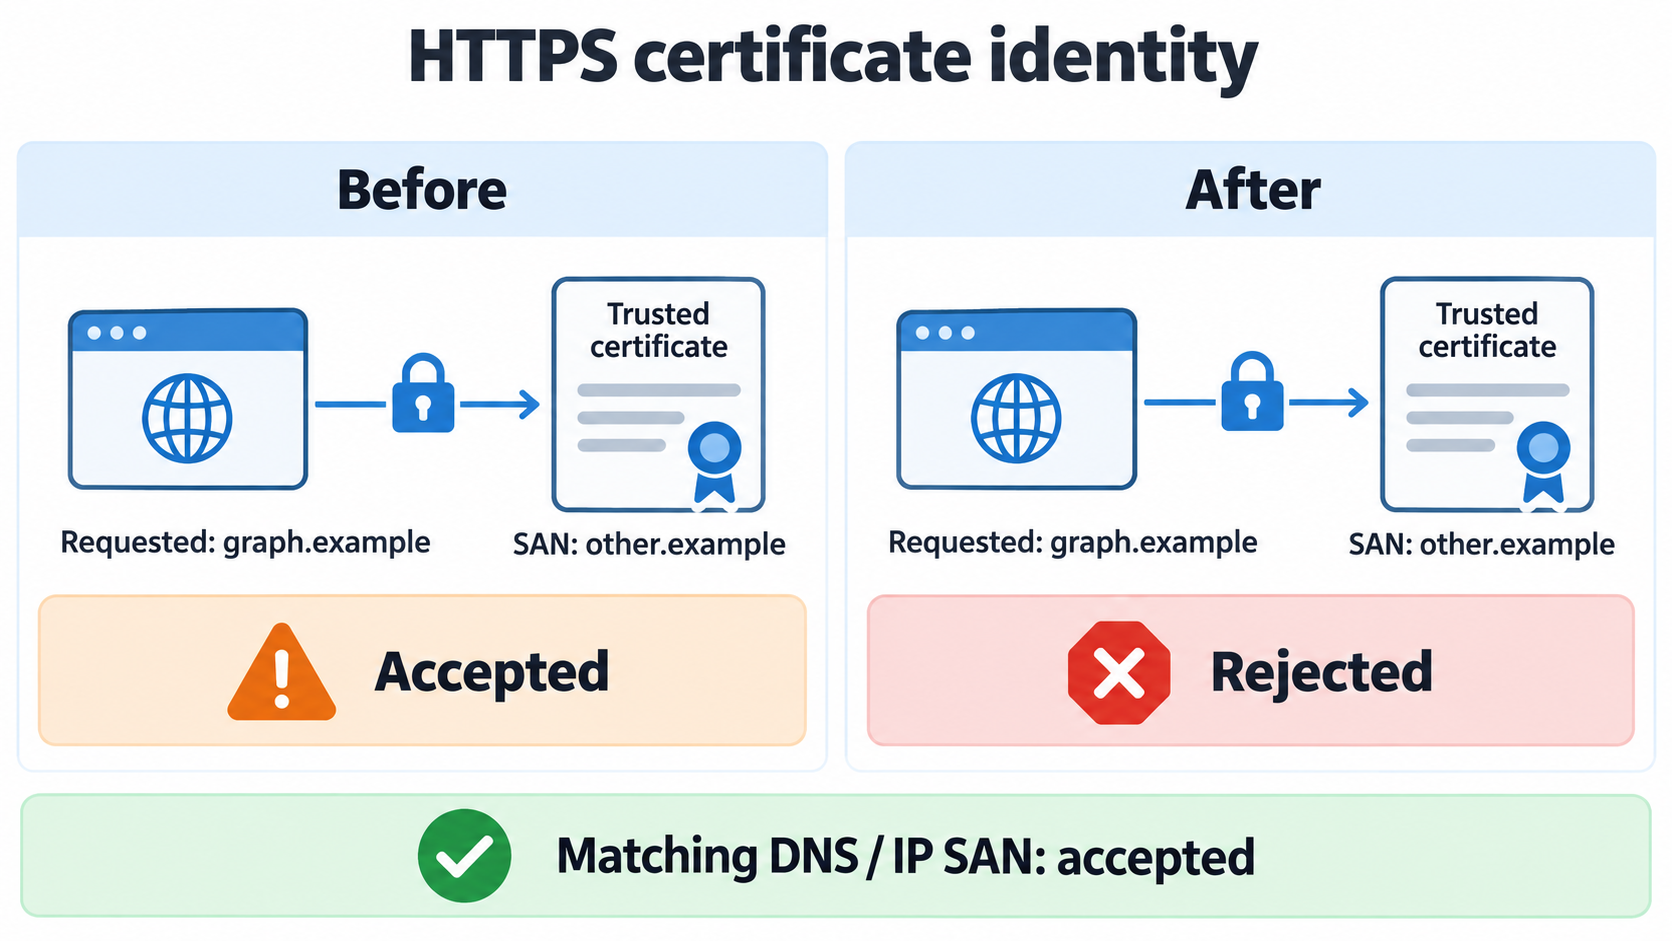 ## Main changes - Preserve certificate identity checks when configuring a custom truststore. - Cover real HTTPS handshakes for matching DNS/IP SANs, wrong or missing SANs, and untrusted certificates. - Clarify shared-type and query-serializer import migrations, process-wide namespace constraints, and which distribution outputs `clean` removes. ## Verification Fresh Java 17 compilation, targeted REST tests, style checks and independent reviews pass. The same handshake regression fails with the original verifier because the trusted, wrong-identity certificate is accepted. ## Documentation The Commons README documents the certificate requirement; the migration and contribution guides contain the accompanying corrections. Paired website documentation: [apache/hugegraph-doc#511](https://github.com/apache/hugegraph-doc/pull/511). -- This is an automated message from the Apache Git Service. To respond to the message, please log on to GitHub and use the URL above to go to the specific comment. To unsubscribe, e-mail: [email protected] For queries about this service, please contact Infrastructure at: [email protected] --------------------------------------------------------------------- To unsubscribe, e-mail: [email protected] For additional commands, e-mail: [email protected]

