kohrar edited a comment on issue #6127:
URL: https://github.com/apache/cloudstack/issues/6127#issuecomment-1070322444
The two session cookies have a different path. One has `/client`, and the other has `/client/api`. 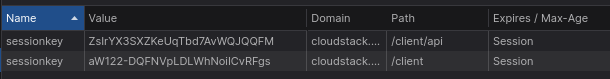 Please correct me if I'm wrong, but I believe the `/client/api` version is the one that should be in use. It's the version that exists when I sign in directly without SAML2. If that's true, the issue here is the `/client` version which is being incorrectly set by when we get redirected back from the SAML2 authentication server which is defined by [`saml2.sp.sso.url`](https://github.com/apache/cloudstack/blob/main/plugins/user-authenticators/saml2/src/main/java/org/apache/cloudstack/saml/SAML2AuthManager.java#L46). Because no path is set, the cookie's path gets set to `/client` based on the URI path. I tried to change this so it included an extra slash (ie. `/client/api?command=samlSso`) but that just made all the other cookies set with the wrong path. I'll try patching in a path for this cookie, which is set in `SAMLUtils.java`, and see if that fixes the issue. -- This is an automated message from the Apache Git Service. To respond to the message, please log on to GitHub and use the URL above to go to the specific comment. To unsubscribe, e-mail: [email protected] For queries about this service, please contact Infrastructure at: [email protected]

