Aman-Mittal opened a new issue, #769:
URL: https://github.com/apache/fineract-backoffice-ui/issues/769
### Summary A user whose only permission is `ALL_FUNCTIONS_READ` (an auditor) sees **enabled** write controls on three admin screens. The platform refuses every write correctly, so this is a frontend-only defect: dead-end controls, the class `rbac-dead-end-controls.spec.ts` exists to catch. Elsewhere the same session is gated correctly. Loan **Approve** and savings **Approve / Decline / Withdrawn by applicant** are disabled with a "Requires …" tooltip, and Clients shows no Create or Edit at all. ### Environment - App: https://aman-mittal.github.io/fineract-backoffice-ui (deployed `main`) - Backend: `sandbox.mifos.community`, tenant `default` - Role: `E2E-AUDIT-20261016 Auditor`, holding exactly `ALL_FUNCTIONS_READ` - 2026-10-16 ### Preconditions A role with only `ALL_FUNCTIONS_READ`, assigned to a user. ### Steps to reproduce 1. Sign in as that user. 2. **Settings → Global Configurations**: click any *Enabled* toggle, or any row's Edit. 3. **Security → Users** and **Security → Roles**: click a row's Edit. ### Expected behavior Toggles and Edit actions are disabled (with the same "Requires UPDATE_CONFIGURATION / UPDATE_USER / UPDATE_ROLE" tooltip used on the loan and savings screens) or hidden. ### Actual behavior | Screen | Control | State | On click | |---|---|---|---| | Global Configurations | 10 *Enabled* toggles per page | enabled | `PUT /configurations/1` → **403**; toasts *"Insufficient privileges to perform this action. • [id] User has no authority to: UPDATE_CONFIGURATION"* and *"Failed to update configuration"*; the toggle reverts | | Global Configurations | row Edit | enabled | opens the *Edit Configuration: maker-checker* dialog with an editable Value and **Save** | | Users | row Edit ×5 | enabled | navigates to `/forbidden?required=UPDATE_USER` | | Roles | row Edit ×4 | enabled | (same pattern; route guarded) | 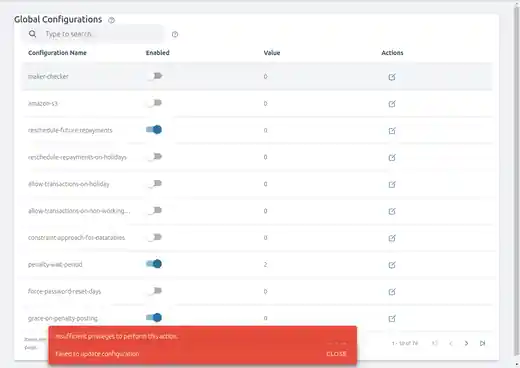 Backend checks from the same session (empty bodies, so nothing was written): `POST /clients`, `POST /loans/1?command=approve`, `POST /savingsaccounts/2?command=approve` and `PUT /roles/3/permissions` all return **403 `error.msg.not.authorized`**. Reads return 200. Backend enforcement is correct. ### Impact Auditors and other read-only staff are invited to change tenant-wide configuration (maker-checker, penalty wait period and similar) and get an error afterwards. On the Users and Roles screens they land on Access Denied. It undermines confidence in the permission model, and on Global Configurations the toggle briefly flips before reverting, which can read as "it changed". ### Suggested investigation Apply `appRequiresPermission` (the directive already used on loan and savings actions) to the configuration toggles and Edit buttons (`UPDATE_CONFIGURATION`), to Users Edit (`UPDATE_USER`) and to Roles Edit (`UPDATE_ROLE` / `PERMISSIONS_ROLE`). Extend `rbac-dead-end-controls.spec.ts` with an `ALL_FUNCTIONS_READ` user. ### Verification status Reproduced. ### Related endpoints `PUT /configurations/{id}`, `PUT /users/{id}`, `PUT /roles/{id}`, `PUT /roles/{id}/permissions` ### Acceptance criteria - With only `ALL_FUNCTIONS_READ`, no enabled control on these three screens sends a write. - An e2e check asserts this for the read-only role. ### Related issues #751 (screens a role can't load), #691, #696. -- This is an automated message from the Apache Git Service. To respond to the message, please log on to GitHub and use the URL above to go to the specific comment. To unsubscribe, e-mail: [email protected] For queries about this service, please contact Infrastructure at: [email protected]

